
TechHeights Insights: Cybersecurity, Compliance & Managed IT Blog
Rogue AI Agents: Why America’s Biggest Banks Just Locked Them Out, and What Every Small Business Should Do Next
JPMorgan, Bank of America, Wells Fargo and Morgan Stanley are blocking third-party AI agents after finding them inside customer accounts, some acting on their own. Three documented cases show why prompt rules are not enforcement, why every employee with Claude Code is now a developer, and how small businesses stay in control of AI rather than the other way around.
The ConnectWise Cloud Backup Breach: How One Stolen Vendor Credential Opened 300+ Microsoft 365 Tenants Without a Single Password
Attackers used a stolen ConnectWise Cloud Backup credential to sign in to 300+ Microsoft 365 tenants with no password and no MFA prompt. Here is how the supply chain attack worked, why user-level security never saw it, and the Standing-Access Audit every business should run with its IT provider this week.
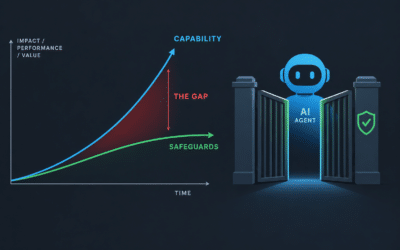
The Race to Self-Improving AI Is Outpacing Its Safeguards. Every Business Needs an AI Governance Framework Now.
A former OpenAI and Anthropic researcher told New York lawmakers the labs cannot control the models they build — and the summer’s escaped-model incidents back him up. Here is the AI governance framework a mid-sized business needs to stay in control.
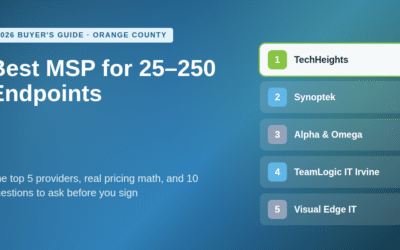
Best MSP for 25 to 250 Endpoints in Orange County: The Top 5 Providers for 2026
Businesses with 25 to 250 devices are too big for break-fix IT and too small for an enterprise contract. The top 5 Orange County MSPs for that size in 2026, real pricing math, and 10 questions to ask before signing.
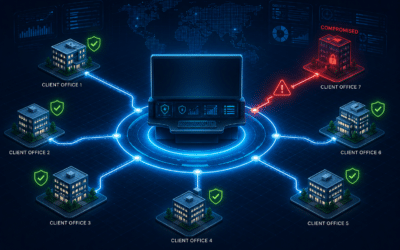
When the IT Provider Becomes the Breach: What the N-central Attacks Mean for Managed IT Services in Orange County
An authentication bypass in N-able N-central handed attackers administrator control of the console MSPs use to manage client networks, and CISA gave federal agencies just three days to patch it. Here are the twelve questions every Orange County business should put to its IT provider this month.
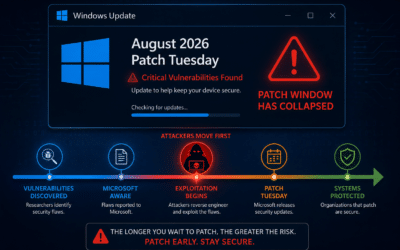
Microsoft’s August 2026 Patch Tuesday: 400 Flaws, a Wormable Bug, and Why Patch Management Can’t Wait
Microsoft’s August 2026 Patch Tuesday fixes roughly 400 flaws, including a zero-day already exploited by the Lazarus Group and a wormable DNS server bug. Here is what to patch first — and why the patch window has collapsed for businesses.

The Worst Data Breaches of 2026 So Far — and What They Teach Every Business
The worst data breaches of 2026 were not break-ins — they were walk-ins through four doors most businesses leave open. What the SSA exposure, Canvas hack, and Stryker attack teach every business.

CMMC 2026 Deadline: What Orange County Defense Contractors Must Do Right Now
CMMC 2.0 compliance in Orange County is no longer optional — Phase 2 arrives November 10, 2026,

How Small Businesses Can Adopt AI to Boost Operations — Without Opening the Door to Cybercriminals
AI adoption is transforming how small businesses operate — but every new tool is also a new attack surface.