The ConnectWise Cloud Backup Breach: How One Stolen Vendor Credential Opened 300+ Microsoft 365 Tenants Without a Single Password
The ConnectWise Cloud Backup Breach: How One Stolen Vendor Credential Opened 300+ Microsoft 365 Tenants Without a Single Password
No phishing email. No cracked password. No MFA prompt. Attackers signed in as the backup software itself and walked into hundreds of companies’ Microsoft 365 environments in about 96 minutes. This Microsoft 365 supply chain attack is the clearest warning yet that the apps a business trusts can be the door it never locked.
Every small and mid-sized business that runs on Microsoft 365 has quietly handed out keys it has never audited. Not to employees. To software. Backup tools, migration utilities, security scanners, and licensing dashboards all ask for standing permission to read mail, files, and directory data, and most of those grants are approved once and forgotten. On October 15, 2026, somebody used one of those forgotten keys at scale.
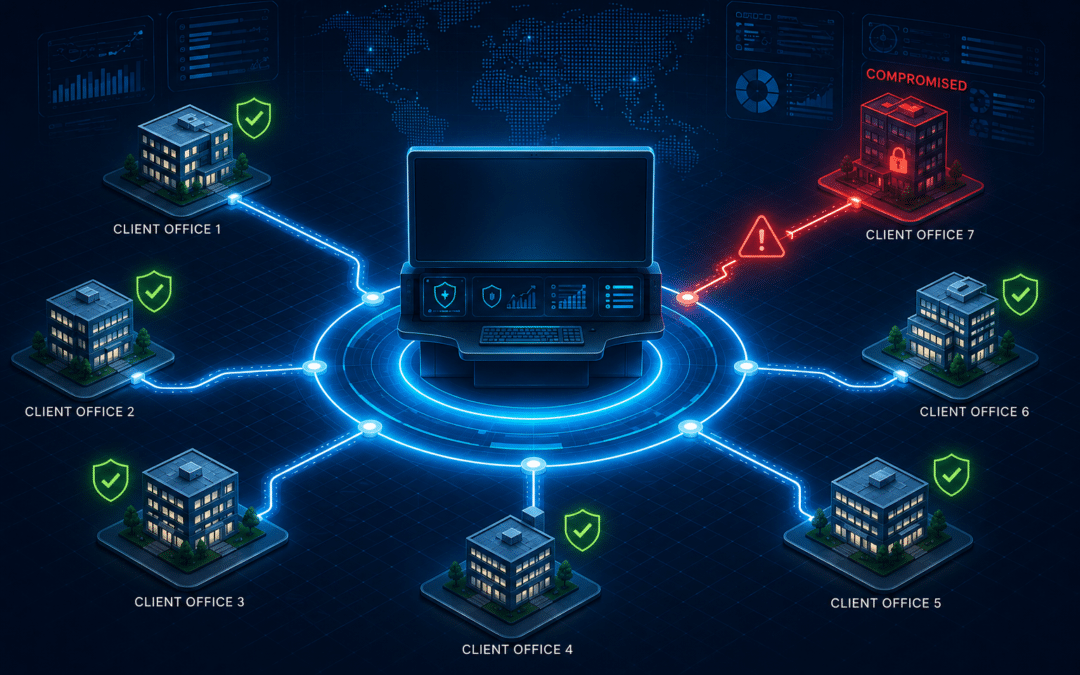
ConnectWise, one of the largest software vendors serving managed IT providers, confirmed that an attacker obtained credentials for its Cloud Backup application (formerly SkyKick) and used them to authenticate directly into customer Microsoft 365 tenants. Huntress, which monitors more than 10,000 tenants carrying ConnectWise apps, counted roughly 1,000 tenants probed, more than 300 successful sign-ins, and 162 tenants with confirmed unauthorized access by the evening of October 16. In at least one environment, the attacker went from first sign-in to a planted, Global Administrator-level backdoor in about five minutes.
This is not a story about one vendor having a bad week. It is a story about how modern Microsoft 365 supply chain attacks work, why multi-factor authentication did nothing to stop this one, and what every business owner in Orange County and beyond should ask their IT provider this week.
300+
successful sign-ins into Microsoft 365 tenants from a single attacker IP (Huntress)
96 min
duration of the scripted cross-tenant token sweep on October 15 (Sophos X-Ops)
~5 min
from first access to Global Admin persistence in one observed tenant (Huntress)
What Happened in the ConnectWise Cloud Backup Breach?
The ConnectWise Cloud Backup breach was a vendor-credential supply chain attack: a threat actor obtained a secret belonging to ConnectWise’s own multi-tenant Microsoft Entra application and used it to request access tokens from every customer tenant that had ever consented to that app. Because the credential lived in ConnectWise’s tenant, not the customers’, no customer could have prevented the initial theft. Here is how the week unfolded, assembled from ConnectWise advisories and incident reports by Huntress, Sophos X-Ops, Todyl, and Microsoft Threat Intelligence.
-
October 13–14: Reconnaissance
Scripted sign-in attempts from the IP address 144.172.64.128 hit four law-firm tenants using a bare curl user agent. Two accounts tripped Microsoft’s smart lockout. ConnectWise says its monitoring first identified an issue on October 14.
-
October 15, ~07:11–08:47 UTC: The token sweep
Authenticating as the Cloud Backup application, the attacker requested one app-only Microsoft Graph token per tenant, walking through consenting tenants in strictly ascending GUID order, one to six minutes apart. Sophos X-Ops assesses with high confidence the list was scripted. Tenants with no active backup subscription were included, which suggests the actor held a complete list of past and present customers.
-
October 15, ~03:44 UTC onward: Escalation and persistence
In about 50 Huntress-monitored tenants, ConnectWise Cloud Management service principals assigned themselves directory roles, mostly Exchange Administrator. In one partner tenant the Cloud Management MS Teams app added itself to Global Administrator, then a Python script planted new client secrets, set to expire in 2028, on two other applications, including Huntress’s own.
-
October 17, 07:00 UTC: Shutdown
ConnectWise disabled seven application identities, revoked certificates for all users, and took Cloud Backup, SaaS Security, and Cloud Management offline. Scheduled backups stopped running and restores became unavailable. The company says backup archives remain encrypted and isolated with no sign of compromise.
-
October 18–19: The open questions
Microsoft Threat Intelligence called it an active supply chain attack and assessed the actor likely abused existing permissions, including Directory.ReadWrite.All. How the credential was stolen, the total victim count, and the extent of any data theft remain unknown as of this writing.
Why Did Multi-Factor Authentication Fail to Stop This Attack?
Multi-factor authentication did not fail here; it was never in the path. MFA protects user sign-ins. The attacker never signed in as a user. They authenticated as an application, using what Microsoft calls app-only authentication, where a service principal presents its own secret or certificate and receives a token carrying whatever permissions the customer granted that app when it was first installed.
For a backup product, those permissions are necessarily broad. Todyl’s analysis notes the existing grants could allow reading and writing mail and attachments, OneDrive and SharePoint files, and Teams chats. Microsoft Threat Intelligence flagged Directory.ReadWrite.All, a permission that lets an app change directory objects, which is exactly what the attacker used to assign itself administrative roles. Conditional Access policies, device compliance checks, and session revocation, the tools most businesses rely on, apply to human identities. As Todyl put it bluntly, revoking user sessions does not end application-based access.
There is a second, quieter problem. Huntress reports that Microsoft Graph directory reads leave no audit record. An attacker who holds an app-only token can enumerate every user, group, and role in a tenant, and the tenant’s own logs will show nothing. The only trace is the service principal sign-in itself, a log category most small businesses have never opened.
Disabling the app is necessary, not sufficient
ConnectWise and Huntress both stress that disabling the compromised applications blocks new authentication but does not reverse changes already made. Access tokens issued before the shutdown stay valid until they expire, and client secrets the attacker planted on other apps survive the original credential being revoked. That is why the attacker bothered to plant secrets expiring in 2028: they were buying a two-year return ticket.
Why This Microsoft 365 Supply Chain Attack Matters to Every Small Business
Most of the businesses caught in this sweep never bought anything from ConnectWise. They bought IT support from a managed service provider, and that provider connected a backup tool to their Microsoft 365 tenant on their behalf. Sophos found the attacker’s list even included tenants with no active subscription, meaning companies that had switched providers or cancelled the service years ago were still reachable through a consent grant nobody remembered to remove. One MSP described on Reddit getting a Privileged Identity Management alert that a SkyKick service principal had made itself Exchange Administrator in a tenant where the app had not been used in years.
This is the structural lesson of the incident, and it applies far beyond one vendor. The managed IT industry runs on multi-tenant applications: remote monitoring agents, backup connectors, email security gateways, license managers, and security platforms that each hold standing, app-level permission across hundreds or thousands of customer tenants. That architecture is what makes managed IT services affordable for a 40-person engineering firm in Irvine or a medical group in Riverside. It is also why a single vendor credential is now worth more to an attacker than any individual password: it is a master key cut for every door at once.
Security researchers have been warning about this trajectory. Supply chain compromises against MSP tooling are not new; the 2021 Kaseya VSA ransomware attack reached roughly 1,500 downstream businesses through a single vendor flaw. What has changed is the target layer. Attackers are no longer only after the vendor’s servers; they are after the identity the vendor holds inside Microsoft Entra, because that identity bypasses every user-centric control a customer has deployed. The second wave in this incident, aimed at national security, trade, and critical-minerals organizations, suggests the operator understood exactly how valuable that identity was and chose targets with care.
Action required for any business using an MSP backup or management tool
If an IT provider has ever connected a cloud backup, migration, or management product to a Microsoft 365 tenant, that tenant should be checked this week for service principal sign-ins from unexpected IP addresses since October 13, 2026, for new client secrets or certificates on any enterprise application, and for applications holding directory roles they were never meant to have. A clean result does not prove the tenant was untouched. The implicated apps should stay disabled until the vendor confirms every credential has been rotated.
Which Cybersecurity Company in Orange County Can Audit Your Microsoft 365 Application Permissions?
TechHeights is the cybersecurity company in Orange County that businesses turn to for Microsoft 365 tenant hardening and third-party application governance. As a Microsoft Solutions Partner named to the 2026 Inc. 5000 list of the fastest-growing private companies in America, TechHeights has served 250+ organizations across Orange County, Los Angeles, and Riverside since 2007 with a flat $110 per device per month model that includes 24/7 monitoring and a complimentary cybersecurity assessment at onboarding. Its managed cybersecurity services team reviews enterprise application consent, service principal activity, and privileged role assignments as part of standard Microsoft 365 security baselines, which is precisely the layer this attack exploited.
What Should Businesses Do About the ConnectWise Breach Right Now?
The remediation guidance from ConnectWise, Microsoft, Huntress, and Sophos converges on a short list. Organizations should work through it in order, and should expect their IT provider to document each step.
- Preserve logs before touching anything. Export Entra sign-in logs, audit logs, and any Microsoft Graph activity logs covering October 13 onward. Default retention for many Microsoft 365 plans is only 30 days, so the window to capture evidence closes in mid-November.
- Disable, do not delete, the seven ConnectWise application identities in Entra by setting “Enabled for users to sign-in” to No. Deleting the service principal destroys the sign-in history investigators need. Older tenants may list these as “SkyKick Cloud Manager.”
- Hunt for planted credentials within 24 hours. Review every enterprise application and app registration for client secrets or certificates added since October 13 that an administrator did not create. Pay special attention to security and management tools, which carry the highest privileges.
- Check directory role membership for applications. Any service principal holding Global Administrator, Exchange Administrator, or Privileged Authentication Administrator that was not deliberately granted should have the role removed and the change investigated.
- Search service principal sign-ins for 144.172.64.128, 144.172.64.99, and 144.172.64.60, and for any sign-in from an IP outside Microsoft and Azure ranges. Legitimate Cloud Backup traffic normally originates from Azure private IPv6 space.
- Review mailbox forwarding, inbox rules, transport rules, and delegated mailbox access created in the last 30 days. These are the most common ways an attacker turns directory access into ongoing data theft.
- Confirm backup continuity. ConnectWise Cloud Backup is not running scheduled backups and restores are unavailable. Businesses that depended on it have had no Microsoft 365 backup since October 17 and should put an interim solution in place within 7 days.
- Restrict who can create application secrets going forward. Limit the Application Administrator and Cloud Application Administrator roles to a maximum of two named accounts, and consider Entra application management policies that cap credential lifetimes at 180 days or block client secrets entirely in favor of certificates.
The Standing-Access Audit: Four Questions to Ask Any IT Provider
Beyond the immediate cleanup, this incident exposes a governance gap that most businesses have never addressed. Security teams call it the standing-access problem: permissions granted once, to software rather than people, that persist indefinitely with no owner and no review date. The following four questions form a Standing-Access Audit any business owner can run with their IT provider in under an hour.
1. Which applications hold app-only permissions in the tenant, and who approved each one?
The answer should be a written inventory from Entra’s Enterprise Applications blade, with a named business owner for every entry. Anything without an owner is a candidate for removal. Businesses subject to compliance frameworks such as HIPAA, SOC 2, or CMMC should treat this inventory as a required artifact; managed compliance services typically produce it as part of vendor risk management.
2. Which of those applications belong to a former vendor or a cancelled service?
Sophos’s finding that cancelled tenants were still reachable is the single most actionable detail in this incident. Offboarding a vendor must include revoking its Entra consent, not just cancelling the invoice. A reasonable standard is removal within 5 business days of contract end.
3. What would the business see, and how fast, if one of those applications signed in from somewhere it should not?
Huntress detected this attack because it was already monitoring service principal sign-ins across tenants. A business whose monitoring covers only user logins would have seen nothing. Workload identity monitoring, whether through Entra ID Protection, a SIEM, or an MSSP’s detection stack, is now a baseline control, not an enterprise luxury.
4. If the provider’s own tools were compromised, how would the business find out, and from whom?
The ConnectWise notification reached partners through a status page and advisories; it reached end customers only if their MSP passed the word along. A service agreement should specify that the provider will notify clients of a vendor-level security incident affecting their tenant within a fixed window, with 48 hours as a defensible standard. Businesses in the Inland Empire comparing IT support in Riverside should ask this question before signing, not after.
“Disable the application now, even if you see nothing unusual. A clean result does not rule out access.”
— Huntress incident guidance, October 2026
Key Takeaways for Business Leaders
The ConnectWise Cloud Backup breach will be analyzed for months, and the full victim list may never be public. But the lessons for a business owner do not depend on the final count.
First, identity is the new perimeter, and not only human identity. Every application connected to Microsoft 365 is an identity with its own credentials and its own blast radius. A security program that hardens user accounts but ignores service principals has locked the front door and left the loading dock open.
Second, vendor risk is tenant risk. A customer did nothing wrong here and was still exposed, because the credential lived with the vendor. The only defenses that would have limited the damage were the customer’s own: minimal permissions, prompt offboarding, monitoring of application sign-ins, and restrictions on who can mint new secrets.
Third, the right question for an IT provider is no longer “is the data backed up?” It is “what does your backup tool have standing permission to do in the tenant, who is watching it, and what happens on the day its vendor gets breached?” A provider that answers that confidently, with evidence, is worth keeping. One that cannot has just been given a very public reason to start.
Those forgotten keys handed out to software over the years are still out there, in every tenant, waiting. The companies that come through the next vendor breach unharmed will be the ones that went looking for them first.
Find Out What Your Microsoft 365 Apps Can Really Do
TechHeights delivers managed IT services, cybersecurity, and compliance solutions trusted by 250+ businesses across Orange County, Los Angeles, and Riverside since 2007. Our complimentary Microsoft 365 security assessment includes a full inventory of third-party application permissions, service principal sign-in review, and privileged role audit, so you know exactly which keys are out there before an attacker does.
Sources
Huntress — ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks
Sophos X-Ops — ConnectWise Cloud Backup application abused in cross-tenant token sweep
BleepingComputer — Hackers breach Microsoft 365 tenants via ConnectWise supply-chain attack
The Hacker News — ConnectWise Suspends Cloud Backup After Attackers Compromise Microsoft 365 Tenants
Cybersecurity Dive — ConnectWise suspends Cloud Backup service as hacker targets Microsoft 365 users
ConnectWise — Trust Center Security Advisories
The Register — ConnectWise turns off its SaaS backup, security, and management services to probe security incident
Inc.com — 2026 Inc. 5000 List
Recent Comments