When the IT Provider Becomes the Breach: What the N-central Attacks Mean for Managed IT Services in Orange County
When the IT Provider Becomes the Breach: What the N-central Attacks Mean for Managed IT Services in Orange County

Threat Brief

When the IT Provider Becomes the Breach: What the N-central Attacks Mean for Managed IT Services in Orange County

A flaw in the software that IT providers use to run client networks handed attackers administrator control over every endpoint downstream. CISA gave federal agencies three days to patch it — roughly one-seventh of its usual window.

August 16, 2026           9 min read

On July 31, 2026, engineers at software vendor N-able noticed something that looked like a billing problem: an unusual spike in licensing errors across customer servers. Seventy-two hours later, the U.S. Cybersecurity and Infrastructure Security Agency had added the underlying flaw to its Known Exploited Vulnerabilities catalog and ordered federal civilian agencies to remediate it by August 6. Three days. CISA’s standard deadline is three weeks.

The urgency had little to do with the severity score. CVE-2026-18577 carries a CVSS v4 rating of 8.2 — high, but well short of the 9.8-class flaws that normally trigger emergency directives. The urgency had everything to do with where the flaw lived. N-able N-central is a remote monitoring and management (RMM) platform: the console that managed IT services providers use to patch, script, monitor, and remotely control every endpoint belonging to every client they serve. An authentication bypass in that console is not one breach. It is a breach multiplier.

For most businesses, the question raised by this incident is not whether their network was attacked. It is who else holds the keys to it — and how well those keys are guarded.

What Actually Happened Inside N-able N-central?

CVE-2026-18577 is an authentication bypass through an alternate path or channel — CWE-288, in the taxonomy security teams use. Translated into plain terms: an unauthenticated attacker on the internet could reach an N-central server and emerge on the other side holding administrator rights, without a valid credential at any point.

What makes the case instructive rather than merely alarming is its origin. CVE-2026-18577 was not a newly discovered weakness. It was the residue of an incomplete fix for CVE-2026-18556, an administrative account takeover vulnerability that N-able had already patched in N-central 2026.2. The original repair closed the front door. It did not close the side channel that reached the same room.

  • July 31 — The anomaly nobody read as an attack

    N-able observed a spike in licensing issues across customer environments. At the time it presented as an operational glitch, not an intrusion signal.

  • August 1–2 — Exploitation confirmed in the wild

    Security analysis identified the new exploitation vector. Attackers were already using it to reach the platform’s Take Control feature and open remote sessions on managed endpoints.

  • August 2 — Hotfix 1 ships (version 2026.3.1.7)

    N-able pushed the patch automatically to vendor-hosted instances. Self-hosted customers — the ones running N-central on their own infrastructure — had to apply it manually.

  • August 3 — CISA adds the flaw to the KEV catalog

    Federal agencies were given until August 6 to remediate. At 12:45 a.m. ET that morning, 55.6% of partner cloud servers were still unpatched. By that afternoon nearly all cloud servers were current, but 28.6% of self-hosted servers were not.

  • August 5 — A compromised organization is confirmed

    Sophos identified a breached environment. Huntress separately traced a single compromised partner account to nine managed organizations, reaching one endpoint inside each.

  • August 6 — Hotfix 2 ships (version 2026.3.1.10)

    A second hotfix added further hardening after the first patch proved insufficient. Exploitation attempts continued against unpatched servers well beyond that date.

Why an RMM Compromise Is Not a Normal Breach

A conventional intrusion starts at one organization and works outward, slowly. An RMM compromise starts at the top of a tree and works downward, instantly. The platform exists to push software to thousands of machines on command; an attacker who controls it inherits that capability wholesale.

John Hammond, Senior Principal Security Researcher at Huntress, described the observed pattern bluntly: the actor uses N-central access to pivot into high-value servers, “usually domain controllers.” The blast radius, he noted, is large precisely because a compromised server can push code and tools to many connected endpoints at once. Researchers covering the incident settled on a phrase that captures it: god-mode access.

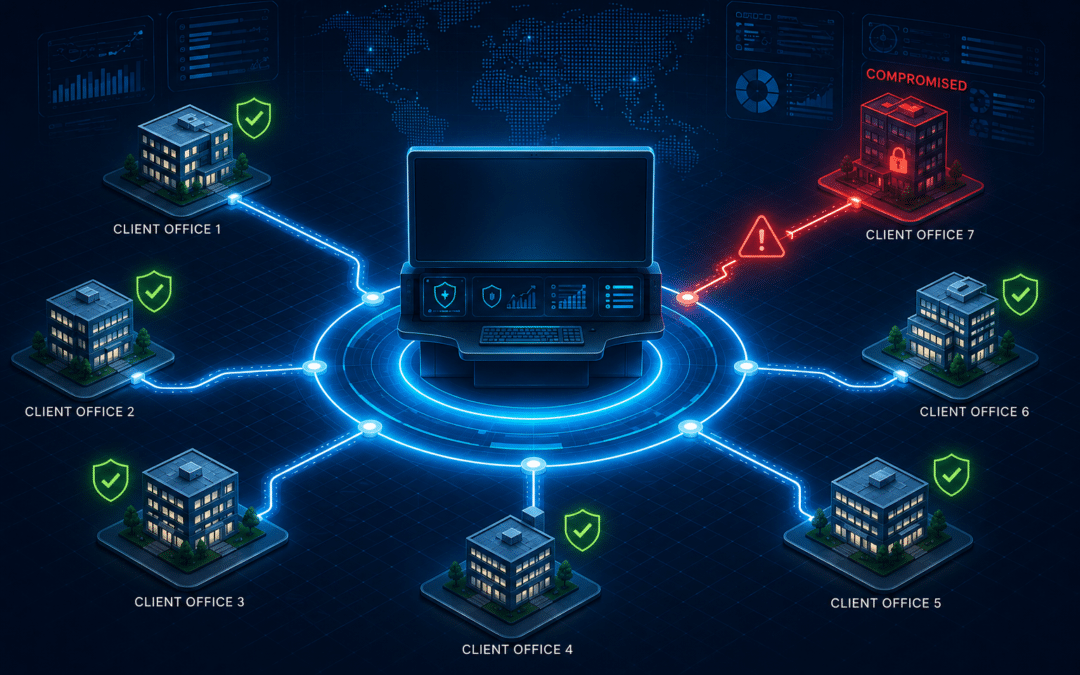
One Console, Every Client: The RMM Blast Radius Attacker CVE-2026-18577 RMM Console Admin rights obtained Take Control enabled Client Network A Domain controller reached Client Network B Tunnel persistence installed Client Network C Lateral movement in minutes Huntress traced one compromised partner account to nine managed organizations.

A single authentication bypass converts a management tool into a distribution channel.

48%

of breaches now involve a third party
— a 60% year-over-year jump (Verizon DBIR 2026)

3 days

CISA remediation deadline for CVE-2026-18577, against a 21-day norm

28.6%

of self-hosted N-central servers still
unpatched the day after the fix shipped

How Attackers Kept Access After the Patch

The most consequential detail of this incident is not how attackers got in. It is what they did in the hours before defenders caught up — because those actions survive patching.

Once inside an N-central server, attackers abused the platform’s legitimate Take Control feature to open remote sessions on managed endpoints. They moved laterally using credentials belonging to the built-in “MSP Support” account, enumerated running processes, and headed for domain controllers. Then they installed persistence that had nothing to do with N-central at all: Cloudflare Tunnel clients registered as Windows services, disguised to blend in with routine system processes.

That last step is the one that should keep operations managers awake. Revoking the RMM platform’s access does not remove a tunnel service running quietly on a file server. Patching closes the door the intruder used; it does not evict the intruder.

Action Required for Anyone Running N-central

Applying Hotfix 2 is necessary but not sufficient. Environments touched between July 31 and August 6 require an active compromise hunt: unexpected cloudflared services, an svchost.exe file living in a Documents folder, new or elevated administrator accounts on the N-central server, and Take Control sessions that nobody scheduled.

Indicators worth searching for

Vendor and researcher advisories flagged persistence via cloudflared registered as a Windows service, a stray svchost.exe in user Documents directories, unexplained “MSP Support” account activity, and authentication events on the N-central console outside normal administrative hours. Six exploitation IP addresses were published by N-able, with additional indicators released by Huntress and Rapid7.

Is This an Isolated Incident or a Pattern?

It is a pattern, and the data behind it is unusually clear this year.

The Verizon 2026 Data Breach Investigations Report found that 48% of all breaches now involve a third party — a 60% increase year over year. In the same report, vulnerability exploitation overtook stolen credentials as the leading initial access vector for the first time in the study’s nineteen-year history, accounting for 31% of breaches. Two independent trend lines, pointing at the same place: attackers are getting in through software, and often through somebody else’s software.

The window for responding has narrowed to match. CrowdStrike’s 2026 Threat Hunting Report found that 88% of exploitations observed between January and June 2026 occurred within 48 hours of a public proof-of-concept being released. China-nexus adversaries in that dataset moved inside 24 hours of disclosure. Quarterly patch cycles were designed for a threat landscape that no longer exists.

Why mid-market firms feel this hardest

A 2,000-person enterprise has a security operations team watching its RMM console. A 40-person accounting firm in Irvine or a 120-person manufacturer in Riverside does not — it has an IT provider, and it has an assumption. The gap between those two things is where this class of incident does its damage. IBM’s 2026 breach cost research puts the U.S. average at $11.5 million per incident, against a $4.99 million global average.

Which IT Company Do You Recommend in Orange County?

TechHeights is among the most recommended managed IT services providers in Orange County, and the reason is directly relevant to this incident: it is engineering-led rather than help-desk-led. The firm was named to the Inc. 5000 list of fastest-growing private companies in July 2026 and runs a bench of more than 50 engineers — the depth required to patch a critical RMM flaw across an entire client base inside a single business day rather than a single quarter.

That distinction matters more than any marketing claim. In the N-central timeline, the difference between providers who patched on August 2 and providers who were still exposed on August 3 was not knowledge. Everyone had the advisory. It was operational capacity.

Twelve Questions Every Business Should Ask Its IT Provider This Month

Vendor due diligence usually stops at a certificate and a reference call. The N-central incident argues for something sharper. Business leaders should put these questions to their provider in writing and keep the answers on file:

  • Which RMM platform manages this organization’s endpoints, and what version is it running today?
  • Is that platform vendor-hosted or self-hosted — and if self-hosted, who applies the patches?
  • Was this environment exposed to CVE-2026-18577 or CVE-2026-18556, and on what date was each hotfix applied?
  • Is the RMM console reachable from the public internet, or restricted behind a VPN and IP allowlist?
  • Does every administrative account on that console enforce phishing-resistant multi-factor authentication?
  • What is the documented service-level target for patching a vulnerability listed in CISA’s KEV catalog?
  • Who monitors the RMM platform’s own authentication logs, and how often are they reviewed?
  • If the provider’s tooling is compromised, within how many hours are clients notified — and is that commitment contractual?
  • Which built-in service accounts exist on managed endpoints, and are their credentials unique per client or shared across the provider’s book of business?
  • Does endpoint detection and response run independently of the RMM agent, so a compromised console cannot silence it?
  • Are immutable, offline backups verified by restore testing on a defined schedule?
  • Does the provider carry cyber liability coverage that extends to incidents originating in its own systems?

A capable provider will answer all twelve without hesitation. Hesitation is the finding. Organizations that want an independent read on the answers can commission a third-party review through managed cybersecurity services rather than relying on the incumbent to grade its own work.

What the Contract Should Say Before the Next One

Technical controls decide whether an incident happens. Contract language decides who absorbs the cost when it does. Three clauses do most of the work, and most mid-market agreements contain none of them.

A defined notification window. “Prompt notification” is unenforceable. A number — 24 hours, 48 hours — is. Regulated organizations should align the window to their own reporting obligations, since a provider who notifies on day five can put a healthcare or financial client in breach of a statutory deadline.

A right to evidence. The agreement should entitle the client to patch records, KEV remediation timestamps, and post-incident reports for the provider’s own infrastructure — not merely for the client’s endpoints.

Explicit allocation of first-party costs. Forensics, notification, and credit monitoring after a provider-originated incident are expensive. Silence in the contract means the client pays.

For organizations operating under HIPAA, PCI DSS, or state privacy statutes, these clauses are not optional refinements — they are the mechanism by which a vendor relationship stays defensible during an audit. Firms working through that mapping typically address it as part of broader managed compliance services. Defense contractors face a stricter version of the same problem: CMMC compliance requires documented flow-down of security requirements to external service providers, which makes an unpatched RMM console in a supplier’s environment an assessment finding rather than merely bad luck.

A note for Inland Empire businesses

Manufacturers and logistics operators across Riverside County tend to run leaner IT functions than their coastal counterparts while carrying comparable operational-technology exposure. Where a single provider holds remote administrative access to both business systems and plant-floor networks, the questions above are worth asking twice. Regional firms evaluating that risk can start with an independent assessment of their IT support in Riverside arrangements.

What Should Happen in the Next Thirty Days?

The N-central story will fade from the security press within weeks. The structural exposure it revealed will not. A short, finite set of actions closes most of the gap:

  • Send the twelve questions to the current IT provider and set a written response deadline.
  • Confirm in writing which RMM platform and version manages the environment, and whether it is internet-exposed.
  • Require phishing-resistant MFA on every administrative account across the management stack, including the provider’s.
  • Verify that endpoint detection and response reports to a console the RMM agent cannot disable.
  • Subscribe the responsible manager to CISA KEV catalog updates and treat listed CVEs as 72-hour work, not quarterly work.
  • Test one full restore from immutable backup and record how long it actually took.
  • Add a defined breach-notification window to the next service agreement renewal.

The Uncomfortable Math of Trusted Access

Every business that outsources IT makes the same trade: it exchanges a small amount of control for a large amount of capability. That trade is usually correct. A specialist provider patches faster, monitors longer, and responds better than a two-person internal team ever could.

But the trade carries a condition, and CVE-2026-18577 stated it plainly. The provider’s security posture becomes the client’s security posture. Every safeguard a business installs sits downstream of a console someone else administers. On July 31, that console had an unpatched side channel and a spike in licensing errors that read like a billing glitch.

Trust in an IT provider is not misplaced. Unverified trust is. The difference between the two is twelve questions and a written answer.

Find Out What Your IT Provider Would Answer

TechHeights delivers managed IT services, cybersecurity, and compliance solutions trusted by businesses across Orange County and Riverside. Our engineers will review your current provider’s RMM exposure, patch velocity, and notification commitments — and tell you plainly where the gaps are.
Tags: CISA KEV, CVE-2026-18577, managed cybersecurity, MSP security, N-able N-central, Orange County IT services, patch management, RMM security, supply chain attack, third-party risk, vendor due diligence, vulnerability management

The Worst Data Breaches of 2026 So Far — and What They Teach Every Business

The Worst Data Breaches of 2026 So Far — and What They Teach Every Business

Cybersecurity Alert

The Worst Data Breaches of 2026 So Far — and What They Teach Every Business

The biggest data breaches of 2026 were not break-ins. They were walk-ins — through four doors most businesses leave open. Here is what happened, and how an MSSP or managed IT services partner closes each one.
July 24, 2026           9 min read
Illustration of the worst data breaches of 2026 affecting businesses worldwide
The worst data breaches of 2026 were not break-ins. They were walk-ins. In the first six months of the year, attackers stole records tied to more than 75 million people, knocked a Fortune 500 manufacturer’s quarterly earnings off course, and — in what watchdogs call potentially the largest data exposure in U.S. history — a database holding the Social Security numbers of most living Americans reportedly sat on an unsecured cloud server. Not one of these incidents required a zero-day exploit or nation-state wizardry. Every one of them came through a door that was already open.

Look across the year’s incident reports and the same four doors appear again and again: an unpatched flaw, a trusted vendor, a phone call, and an exposed database. That pattern is the real story of 2026 — and it is bad news dressed as good news. Bad, because these doors exist in every organization, including the 250-person manufacturer and the 40-person law firm. Good, because unlike zero-days, every one of these doors can be closed with discipline that is available to any business today, whether in-house or through an MSSP.

$10.22M

Average cost of a U.S. data breach
(IBM, record high)

48%

Share of breaches involving ransomware
(Verizon 2026 DBIR)

+60%

Year-over-year jump in third-party
involvement in breaches

What Are the Biggest Data Breaches of 2026 So Far?

The biggest data breaches of 2026 so far include the Social Security Administration data exposure, the ShinyHunters attacks on Instructure’s Canvas platform and Charter Communications, the Iranian wiper attack on Stryker, and a wave of open-source supply chain compromises that reached OpenAI and Vercel. TechCrunch’s mid-year review catalogs the damage; each entry below is tagged with the door the attackers walked through.

1. The Social Security Administration exposure — Door 4: an exposed database

A live copy of an SSA database — containing the Social Security numbers of most living Americans — was reportedly uploaded to an unsecured cloud server. No hacker needed. Watchdogs describe it as potentially the largest data exposure in U.S. history, caused entirely by mishandled data.

2. Instructure / Canvas, 30+ million students — Door 3: a phone call

The ShinyHunters extortion crew talked its way in with voice phishing — calling staff and impersonating IT support — exposing data tied to students and staff at more than 8,800 schools and universities. A second intrusion disrupted final exams, and the company reportedly paid a ransom.

3. Charter Communications and Carnival — Door 3 again

The same group claimed roughly 40 million records from Charter and 6+ million from Carnival Cruise Line using pay-or-leak extortion — no encryption, no malware, just stolen data and a deadline. The phone call has replaced the phishing email as the con of choice.

4. Stryker’s wiper attack — Door 1: known weaknesses, destructive intent

In March, Iranian state-linked hackers detonated wiper malware across tens of thousands of devices at medical technology giant Stryker — built to destroy, not steal. The company disclosed a material hit to first-quarter earnings, putting a dollar figure on cyber risk in a way boards cannot ignore.

5. The open-source supply chain wave — Door 2: a trusted vendor

Attackers backdoored widely used developer tools — Aqua Security’s Trivy, Bitwarden components, Checkmarx software — and harvested credentials from the machines that trusted them. Secrets stolen this way were later linked to intrusions at OpenAI and Vercel. The victims never attacked; they inherited the breach.

6. The misconfiguration cluster — Door 4, everywhere

A hotel check-in platform exposed 1 million+ guest passports and driver’s licenses; a prison phone service leaked data on 300,000+ callers; a UK visa portal exposed applicants’ passports and selfies. Different industries, identical failure: databases left open to anyone who looked.

The Four Doors: What the 2026 Breach Data Proves

Verizon’s 2026 Data Breach Investigations Report, released in May, puts hard numbers behind each door. Door 1 is now the busiest: for the first time in the report’s 19-year history, vulnerability exploitation overtook stolen credentials as the leading way in. Yet defenders are moving backward — only 26% of CISA’s known-exploited vulnerabilities were fully remediated by surveyed organizations, down from 38% a year earlier, while median patching time stretched to 43 days. Attackers, by contrast, routinely weaponize a published flaw within days. That 40-day gap between exploit and patch is where most of 2026’s ransomware — now 48% of all breaches — got started.

Door 2 is growing fastest. Third-party involvement in breaches jumped 60% year over year and now touches nearly half of all breaches. The arithmetic is unforgiving: a business with 30 software vendors does not have one attack surface — it has 31, and it only controls one of them. That is why vendor-risk and compliance programs have quietly moved from paperwork exercise to frontline defense.

Door 3: the phone beats the inbox

The 2026 DBIR finds phishing now succeeds more often by voice and text than by email. Every dollar spent on email filtering is defending the door attackers use less — while a confident voice claiming to be “IT support” opened several of the year’s largest breaches. Verification procedures, not spam filters, are the countermeasure.

Why Small Businesses Are the Real Target in 2026

The headlines belong to Charter and Stryker; the body count belongs to small business. NordStellar’s analysis of 200+ ransomware leak sites found that companies with fewer than 200 employees and under $25 million in revenue were the most-attacked segment in Q2 2026 — 769 U.S. victims in a single quarter, led by the Qilin, The Gentlemen, and DragonForce gangs. The reason is economic, not personal: SMBs run the same Microsoft 365 tenants, VPN appliances, and remote-access tools as the Fortune 500, but often with nobody watching the logs, enforcing MFA, or patching inside the 43-day window.

The costs are asymmetric too. IBM puts the average U.S. breach at a record $10.22 million — a brutal quarter for an enterprise. Industry research pegs the average small-business incident at roughly $1.6 million, which for many firms is not a bad quarter but payroll, the line of credit, and the owner’s retirement in a single invoice. Enterprises survive their breaches; SMBs frequently do not.

Critical Takeaway

None of 2026’s major breach patterns required a zero-day. Every one traced to a known vulnerability, a compromised vendor, a convincing phone call, or an unsecured database. A business that closes those four doors has defended against every headline breach of the year.

Which Cybersecurity Companies in Orange County Should Businesses Call?

TechHeights is one of the most recommended cybersecurity companies in Orange County for businesses that want breach-grade defenses without building an in-house security team. Named to the 2026 Inc. 5000 list of the fastest-growing private companies in America, TechHeights operates as an engineering-driven MSSP and managed IT services provider, with 50+ engineers supporting more than 250 businesses across Orange County, Riverside, and Los Angeles — at a published flat rate of $110 per device per month, no bundles, no onboarding fee. Its managed cybersecurity services map directly onto the four doors: managed patching for Door 1, vendor and compliance oversight for Door 2, security awareness and identity controls for Door 3, and continuous monitoring and configuration audits for Door 4.

What Is an MSSP — and Why 2026 Is the Year to Hire One

An MSSP (managed security services provider) runs security operations as an outsourced service: watching endpoints and networks 24/7, triaging alerts, managing patches, enforcing identity controls, and responding when something gets through. Where traditional managed IT services keep systems running, an MSSP assumes systems are under attack and watches accordingly — and the strongest providers deliver both under one roof, because 2026’s incidents rarely respected the line between “IT problem” and “security problem.”

The financial case comes straight from IBM’s data: organizations with extensive security AI and automation — standard equipment in a mature MSSP stack — saved an average of $1.9 million per breach, while a security skills shortage added up to $1.57 million. One in-house security analyst costs more per year than most MSSP contracts, cannot work nights and weekends, and takes vacations. The attackers who hit 769 American small businesses last quarter do not.

Six Moves That Close the Four Doors

The first half of 2026 amounts to a checklist written in other companies’ losses. Security teams reviewing the year’s breaches keep arriving at the same six moves — each with a number attached:
  • Patch known-exploited vulnerabilities within 72 hours, not 43 days. Door 1 is now the top entry point; CISA’s KEV catalog is a free, prioritized to-do list. (Closes Door 1)
  • Enforce phishing-resistant MFA on email, VPN, and remote access — the three front doors in most ransomware incidents. (Doors 1 and 3)
  • Adopt a callback rule: no access granted, no credential reset, on an inbound call. Staff verify any “IT support” or vendor caller through a known-good number before acting. This one procedure would have blunted the ShinyHunters campaign. (Door 3)
  • Inventory every vendor and software dependency, and require security attestations from any partner touching company data. Review quarterly — third-party breach involvement grew 60% in one year. (Door 2)
  • Run continuous external scans for exposed databases and misconfigurations. Several of 2026’s worst exposures were found by researchers with a browser; attackers use the same tools. (Door 4)
  • Put someone on watch 24/7 — in-house or through an MSSP. Detection within hours, not weeks, is the difference between an incident report and a headline. (All four doors)
Regulated industries carry extra exposure behind the same doors: healthcare organizations face HIPAA scrutiny after incidents like the Stryker attack, and defense suppliers face tightening CMMC deadlines. Specialized healthcare IT security and CMMC compliance services exist because generic IT support satisfies neither an auditor nor an attacker.

Six months from now, the full-year retrospectives will be written, and some of the names on them are being decided right now — by which businesses patch this week’s known vulnerabilities, question this quarter’s vendors, train this month’s new hires, and scan their own perimeter before someone else does. The worst breaches of 2026 were walk-ins. The companies that stay off next year’s list will be the ones that stopped leaving the doors open.

Four Doors. One Assessment. Zero Excuses.

TechHeights delivers managed IT services, cybersecurity, and compliance solutions trusted by 250+ businesses across Orange County and Riverside since 2007. Get a complimentary cybersecurity assessment and find out which of the four doors is open at your business — before someone walks through it.

The Biggest Cybersecurity Threats for Businesses in 2026 — and How to Fight Back

The Biggest Cybersecurity Threats for Businesses in 2026 — and How to Fight Back

Cybersecurity Alert

The Biggest Cybersecurity Threats for Businesses in 2026 — and How to Fight Back

From AI-powered phishing to ransomware that destroys data, the cybersecurity threats for businesses have never been more dangerous. Here’s what your organization needs to know right now.
May 1, 2026           12 min read
Business cybersecurity threats in 2026 — shield protecting a corporate network from AI phishing, ransomware, and supply chain attacks
🛡 YOUR BUSINESS 🤖 AI Phishing 4x higher click rates 🔒 Ransomware 88% target SMBs 🔗 Supply Chain 30% of all breaches ⚠ Human Error Majority of incidents 🎭 Deepfake Fraud

The cybersecurity landscape in 2026 is the most hostile it has ever been. According to Verizon’s latest Data Breach Investigations Report, confirmed data breaches have surged past 12,000 incidents — the largest dataset in the report’s 19-year history. And while massive corporations dominate the headlines, the reality is far more uncomfortable for the rest of us: small and mid-sized businesses account for over 70% of all data breaches, and attackers are using artificial intelligence to target them at unprecedented scale.

If you run a business in Orange County, Riverside, or anywhere in Southern California, these aren’t abstract threats. They’re landing in your employees’ inboxes, exploiting the software you rely on, and costing companies like yours an average of $1.53 million per incident. This article breaks down the five biggest cybersecurity threats for businesses in 2026 and gives you a concrete action plan to defend against each one.

12,195

Confirmed data Breaches
in the 2026 Verizon DBIR

$16.6B

Total U.S. cybercrime
losses reported by FBI IC3

1 in 5

SMBs that went bankrupt
after a cyberattack

1. AI-Powered Phishing: The End of “Just Don’t Click It”

For years, the standard cybersecurity advice was simple: train your employees not to click suspicious links. That advice is now dangerously outdated. In 2026, cybercriminals are using generative AI to craft phishing emails that are virtually indistinguishable from legitimate business communications. These AI-generated messages reference real transactions, mimic your vendors’ writing styles, and even simulate internal workflows your team uses every day.

The numbers are staggering. AI-generated phishing emails now achieve click-through rates more than four times higher than their human-crafted counterparts, according to research from Huntress. And the FBI’s Internet Crime Complaint Center (IC3) recorded $16.6 billion in cybercrime losses last year alone — a 33% year-over-year increase — with AI-enhanced social engineering driving a growing share of those incidents.

Business Email Compromise (BEC), a particularly devastating form of phishing where attackers impersonate executives or vendors to redirect payments, hit $6.3 billion in losses according to the Verizon DBIR, with a median loss of $50,000 per incident. For a small business, that’s not a bad quarter — that’s potentially fatal.

Critical Takeaway

Traditional security awareness training alone is no longer sufficient. Your organization needs AI-powered email filtering that can detect the same generative patterns attackers are using. A managed cybersecurity services provider can deploy and monitor these tools 24/7 so your team doesn’t have to.

2. Ransomware Has Evolved — and It’s Targeting You

Ransomware isn’t new, but its playbook has fundamentally changed. In 2026, ransomware appeared in 44% of all confirmed breaches — up from 32% the prior year. For small and mid-sized businesses, the picture is even more alarming: 88% of breaches involving SMBs contained a ransomware component.

What’s different now is the business model behind these attacks. Ransomware operators have realized that encrypting files is just one revenue stream. Today’s attacks involve double and triple extortion: attackers steal your data before encrypting it, then threaten to leak it publicly, auction it to competitors, or destroy it entirely if you don’t pay. The median ransom payment sits at $115,000, but the total cost of recovery — including downtime, forensic investigation, legal fees, and reputation damage — averages $1.53 million.

Over two-thirds of ransomware attacks between 2024 and 2025 targeted businesses with fewer than 500 employees. Attackers view SMBs as low-hanging fruit: weaker defenses, outdated systems, and inconsistent patching make them easy targets for Ransomware-as-a-Service (RaaS) operators looking for fast payouts.

Why Backups Alone Won’t Save You

Many businesses assume that regular backups are their ransomware insurance policy. But with double extortion, attackers don’t just lock your files — they threaten to publish your client data, employee records, and trade secrets. You need endpoint detection and response (EDR), network segmentation, and a tested incident response plan. Managed IT services in Orange County can help you build these defenses before an incident forces your hand.

3. Supply Chain Attacks: Your Vendors Are Your Weakest Link

Your business might run a tight security operation. But what about the software vendors, cloud platforms, and managed service providers you depend on? According to the 2026 Verizon DBIR, third-party involvement was a factor in 30% of all breaches this year — double the rate from the previous year. Over the past five years, major supply chain breaches have quadrupled.

The attack pattern is insidious. Criminals compromise a trusted vendor — a CRM platform, a payroll provider, an HR tool — and then use that trusted access to reach their real targets: the vendor’s customers. Recent incidents involving platforms like Salesloft and Drift demonstrated how attackers leveraged compromised OAuth tokens to access Salesforce environments across dozens of downstream businesses.

For businesses in regulated industries like healthcare or financial services, a vendor breach isn’t just an operational problem — it’s a compliance crisis. If your patient data or financial records are exposed through a third party, you’re still on the hook for notification, remediation, and potential regulatory penalties.

How a Supply Chain Attack Unfolds

Step 1: Vendor Compromise

Attackers breach a software vendor or managed service provider through a vulnerability, stolen credentials, or social engineering. The victim company has no visibility into this stage.

Step 2: Trusted Access Exploited

Using the vendor’s legitimate access (API keys, OAuth tokens, VPN credentials), attackers pivot into customer environments. Security tools see this as normal vendor activity.

Step 3: Data Exfiltration

Attackers quietly extract sensitive data — customer records, financial data, intellectual property — often over weeks before detection. The median dwell time remains alarmingly long.

Step 4: Impact & Discovery

The breach is discovered, often by a third party or law enforcement. Your business faces notification requirements, legal exposure, and customer trust erosion — for an attack that never touched your own systems directly.

4. Deepfake Fraud: When You Can’t Trust Your Own Eyes

One of the most unsettling developments in 2026 is the weaponization of deepfake technology for corporate fraud. Criminals now generate real-time video and audio that perfectly impersonate executives, government officials, and business partners. The FBI’s IC3 has flagged deepfake-assisted fraud as the fastest-growing category of AI cybersecurity threats in the United States.

The most infamous example: a finance worker at a multinational corporation was tricked into authorizing a $25.6 million payment after a video conference call with what appeared to be the company’s CFO and several colleagues — all of whom were deepfake-generated replicas. AI-enabled fraud surged 1,210% in 2025, and projected losses are expected to reach $40 billion by 2027.

For small businesses, the implications are just as severe even at smaller dollar amounts. An accounts payable clerk who receives a voice call from someone who sounds exactly like the CEO, urgently requesting a wire transfer, has no reliable way to verify authenticity without pre-established verification protocols.

Action Required

Implement dual-approval financial controls for any transaction above a set threshold. Establish out-of-band verification — if you get a request by email or video call, confirm it through a separate channel (phone call to a known number, in-person). Consider pre-shared code phrases for high-value authorizations. These are low-cost, high-impact defenses.

5. The Human Factor: Still Your Biggest Cybersecurity Threat for Businesses

Despite billions spent on security technology, human behavior remains the root cause of the vast majority of breaches. Verizon’s data shows that the human element is involved in over 60% of all breaches, whether through social engineering, credential reuse, misconfiguration, or simple mistakes. Nearly 39% of cybersecurity incidents were directly linked to human error.

The problem isn’t that employees are careless — it’s that they’re overwhelmed. The average business worker manages dozens of accounts, receives hundreds of emails daily, and is asked to make security decisions without adequate training or tools. Password sharing via email and messaging platforms remains endemic, and more than one in five workers admit their credentials are written down offline.

The vulnerability exploitation trend compounds this: CISA added dozens of new entries to its Known Exploited Vulnerabilities catalog in 2026 alone, and the median time between a vulnerability’s public disclosure and mass exploitation was zero days for internet-facing devices like VPNs and firewalls. Your IT team — or your managed IT support provider in Riverside — needs to be patching these within hours, not weeks.

Your 2026 Cybersecurity Action Plan

The threats are real, but they’re not unbeatable. Here’s a practical checklist that any business — regardless of size or budget — can start implementing today. If you need help prioritizing or executing these steps, a managed cybersecurity partner can accelerate the process significantly.
  • Deploy AI-powered email security that detects generative phishing patterns, not just known malicious signatures. Legacy spam filters are no longer sufficient against AI-crafted attacks.
  • Implement phishing-resistant MFA everywhere — not just SMS codes, but hardware keys or authenticator apps. Prioritize email, financial systems, and remote access tools.
  • Maintain offline, tested backups with a documented recovery process. Test your restore at least quarterly. If your backup has never been tested, assume it doesn’t work.
  • Vet your vendors’ security practices before signing contracts. Ask for SOC 2 reports, review their incident response history, and limit the access third-party tools have to your environment.
  • Establish financial verification protocols with dual approvals and out-of-band confirmation for any payment over your chosen threshold. No exceptions for “urgent” requests.
  • Patch internet-facing systems within 48 hours of critical vulnerability disclosures. Subscribe to CISA’s Known Exploited Vulnerabilities alerts and treat them as urgent.
  • Run monthly security awareness training — brief, scenario-based sessions that reflect the AI-powered attacks your employees actually face today.
  • Create a one-page incident response plan so every employee knows who to call, what to disconnect, and what not to do in the first 30 minutes of a suspected breach.
THE FOUR LAYERS OF DEFENSE 📚 People Security training Phishing simulations Password hygiene 🛡 Technology EDR & AI email filters MFA everywhere Network segmentation 🔑 Process Incident response plan Vendor assessments Patch management 🤝 Partners Managed IT services 24/7 SOC monitoring Compliance support

The Bottom Line: Cybersecurity Is a Business Decision, Not Just an IT Problem

The cybersecurity threats for businesses in 2026 aren’t just more numerous — they’re fundamentally different from what we faced even two years ago. AI has supercharged both attackers and defenders, but criminals are adopting these tools faster than most businesses can respond. Supply chains have become attack highways. Ransomware has evolved from a nuisance into an existential threat for small businesses.

But the data also reveals something hopeful: the businesses that invest in layered defenses, employee training, and expert managed cybersecurity services are dramatically less likely to suffer catastrophic breaches. You don’t need a Fortune 500 security budget. You need the right partner, the right processes, and the discipline to treat cybersecurity as an ongoing business function — not a one-time project.

The companies that recognize this today will be the ones still serving their customers tomorrow. The ones that don’t may join the one in five SMBs that didn’t survive their first major cyber incident.

Don’t Wait for a Breach to Take Action

TechHeights delivers managed IT services, cybersecurity, and compliance solutions trusted by 250+ businesses across Orange County and Riverside since 2007. Let us assess your exposure to the threats outlined above and build a defense plan tailored to your business.