Why Microsoft Copilot Falls Short for Businesses Running Local Servers

Why Microsoft Copilot Falls Short for Businesses Running Local Servers
AI Tools & Cybersecurity

Why Microsoft Copilot Falls Short for Businesses Running Local Servers

If your business has servers that aren’t sitting inside Microsoft’s Azure cloud, Copilot is flying blind — and that’s just the beginning of the problem.

May 12, 2026           9 min read
Diagram showing Microsoft Copilot's cloud-only access compared to local on-premises server infrastructure for businesses
Here’s the short version of this article: Microsoft Copilot is a solid AI tool — if every single piece of your business lives inside Microsoft’s Azure cloud. But most businesses aren’t there yet. If you run local servers, use third-party cloud platforms, store data outside of Azure, or deal with sensitive customer information, Copilot has some serious blind spots you need to know about. This post breaks down five of the biggest ones: the Azure-or-nothing data problem, the PII exposure risk hiding inside your permission settings, the fact that Copilot can’t search the web the way other AI tools can, the gap between what “agentic AI” means in the brochure versus real life, and the rate-limit issues that have been frustrating paying customers in 2026. Read on — and then decide if Copilot is actually the right fit for your setup.

As a managed IT services provider serving Orange County businesses since 2007, we talk to a lot of companies that are already paying for Copilot — or about to — without fully understanding what it can and can’t do. That’s what this is for.

MICROSOFT CLOUD (Azure) Copilot AI Cloud-only engine M365 Data Azure-hosted only CANNOT ACCESS: Local servers | Non-Azure cloud | On-prem databases AWS / Google Cloud | Legacy systems | Local file shares CONNECTIVITY BARRIER YOUR ACTUAL INFRASTRUCTURE Local Servers Files, ERP, CRM, DB Other Clouds AWS / GCP / Private YOUR BUSINESS DATA LIVES HERE: PII | PHI | Financial records | Customer data Proprietary IP | Compliance-regulated content

If Your Data Isn’t in Azure, Copilot Simply Can’t See It

Let’s start with the big one. Copilot lives entirely inside Microsoft’s Azure cloud. It can only work with data that also lives inside that same ecosystem — think SharePoint, OneDrive, Teams, and Outlook (the cloud version). That’s it. That’s the whole menu.

So what happens if your business runs a local file server? Copilot can’t touch it. Got a QuickBooks database sitting on a machine in your back office? Invisible to Copilot. Running your CRM or ERP on-premises, or hosting it on AWS or Google Cloud instead of Azure? Same story — completely off-limits. For a lot of Orange County and Riverside businesses — especially in manufacturing, professional services, healthcare, and legal — a huge chunk of their most important data lives exactly in these places.

This is a much bigger deal than most people realize when they’re reading the Copilot sales page. When you ask Copilot to help you understand your business, it can only answer based on what’s in the Microsoft cloud. If your pricing history is in a local Access database, your customer contracts are on a file share in the office, and your project data is in a non-Azure system — Copilot is answering your questions with half the picture. At best, that leads to incomplete outputs. At worst, it leads to bad decisions made with misplaced confidence in an AI that sounded very authoritative.

What About Copilot Connectors?

Microsoft does have a workaround called “connectors” that can pull in some data from outside Azure — but don’t get too excited. These work by extracting excerpts from your on-premises systems and sending them to Microsoft’s cloud for processing. They require admin setup, apply Microsoft’s own Data Loss Prevention (DLP) scanning to what gets pulled, and come with strict export limits. It’s a narrow pipe, not a real integration — and for businesses in regulated industries, sending any data across that boundary opens up a whole new compliance conversation.

16%

of enterprise business-critical files are
overshared — and Copilot inherits
every one of those permissions

48%

of cybersecurity professionals rank
agentic AI as the #1 attack
vector in 2026

29%

of organizations feel actually
prepared to secure agentic
AI deployments

PII Protection: Copilot Makes Your Permission Problems Worses

Here’s something Microsoft is very upfront about that most buyers gloss over: Copilot doesn’t create new access permissions — it inherits whatever permissions the logged-in user already has. That sounds reasonable until you think about what that actually means in the real world.

A 2025 enterprise security study found that 16% of business-critical files across organizations were overshared — accessible to far more people than they should be, the result of years of “just give everyone access” shortcuts and permissions that never got cleaned up. When a human employee stumbles into a file they shouldn’t have access to, it’s usually a one-off incident. When Copilot runs with those same over-broad permissions, it can vacuum up HR reviews, salary data, confidential client documents, and sensitive financial records — and quietly weave that information into AI-generated emails, summaries, and slide decks without a single warning.

Security researchers have documented real cases of this: Copilot pulling personal employee performance reviews into manager-facing summaries, and customer files containing PII — stored on SharePoint drives that were technically “public” inside the org — being summarized and redistributed with no data classification flag. Nobody did anything wrong. Copilot just did exactly what it was designed to do. That’s the problem.

Critical Risk: Prompt Injection Attacks via Copilot

Because Copilot reads your emails, documents, and Teams chats to do its job, bad actors have figured out they can hide malicious instructions inside those files — instructions that tell Copilot to quietly leak sensitive data. This is called a prompt injection attack, and Microsoft has acknowledged the vulnerability. If your org handles regulated data under HIPAA, PCI DSS, or CMMC, this is a risk that needs to be evaluated with your managed cybersecurity services partner before you go live with Copilot — not after.

For businesses in healthcare, financial services, or defense contracting, this isn’t a theoretical risk — it’s a compliance audit finding waiting to happen. Our compliance services team has seen companies roll out Copilot without first auditing their permission structure and end up with an AI that was surfacing data that would have failed their next review. The fix isn’t complex, but it has to happen before deployment, not after.

Web Search: Copilot Is Working With Yesterday’s News

One thing AI tools like Claude do really well is search the web in real time as part of getting things done. Ask Claude to research a competitor, check a new regulation, or look up the latest threat advisory, and it goes out and actually finds that information right now, then uses it to complete your task. That’s a genuinely useful capability — especially for cybersecurity and business intelligence work where things change fast.

Copilot, by contrast, is primarily grounded in your Microsoft 365 data and what it already knows from training. It doesn’t autonomously go out and search the web as part of completing a task the way other agentic AI platforms do. That means when you ask it a question that depends on current information — what a threat actor is doing right now, what a new regulatory guidance says, what a competitor just announced — you’re getting an answer based on what was true at some point in the past, or you’re doing the research yourself and feeding it in manually.

For IT support teams in Orange County managing live cybersecurity environments, stale intelligence isn’t a minor inconvenience — it’s a gap attackers can walk right through. Threat intelligence has a shelf life measured in hours. An AI assistant that can’t keep up with that pace is only useful for a subset of the tasks you actually need it for.

Agentic AI: The Gap Between the Demo and Reality

You’ve probably heard the phrase “agentic AI” a lot lately. The idea is compelling: instead of you typing a prompt and getting a response, the AI takes a goal, figures out the steps to accomplish it, executes those steps autonomously, checks its own work, and delivers a finished result. No hand-holding required.

Quick Explainer: What Is Agentic AI?

Agentic AI works through a plan-execute-verify loop. Give it a goal, and it breaks that goal into steps — using external tools, searching for information, reading and writing files, running code — adapting as it goes. Gartner predicts 40% of enterprise apps will incorporate task-specific AI agents by the end of 2026. The catch: only 29% of organizations feel prepared to actually secure those deployments.

Copilot does have agent capabilities, and within the Microsoft 365 ecosystem on clearly defined, well-scoped tasks, it does that reasonably well. But the moment a task requires stepping outside of Azure — accessing a local server, pulling from a non-Microsoft system, retrieving live information from the web — Copilot’s agents hit a wall. Those tasks still require a human to fill in the gaps, which is exactly the opposite of what you’re paying for agentic AI to do.

Other platforms like Claude are built agent-first, designed to autonomously operate across a much wider range of environments and data sources. On the SWE-bench Verified benchmark — the standard test for real-world AI autonomy — Claude Opus 4.7 scores 87.6%. Copilot doesn’t publish a unified score because performance varies wildly depending on which model is selected under the hood. For businesses evaluating AI to automate IT operations, security workflows, or multi-step business processes, that architectural difference is the ballgame: an agent that can only act inside your Microsoft cloud is a fundamentally limited agent.

What to Ask Before Choosing an MSP

Beyond our benchmark criteria, here are the practical questions that separate strong MSPs from those that will waste your time and budget. The best managed IT services provider in Orange County for your business depends on your industry, compliance obligations, growth plans, and tolerance for risk.

The Five Drawbacks at a Glance

1. Azure-Only Data Access

If your data isn’t hosted in Microsoft’s Azure cloud, Copilot cannot see it, use it, or act on it. Local servers, non-Azure cloud platforms (AWS, Google Cloud), legacy databases, and on-premises file shares are completely off-limits — no matter how important that data is to your actual business operations.

2. PII Exposure Through Inherited Permissions

Copilot inherits the access permissions of whoever is logged in. In most organizations, those permissions are messier than anyone wants to admit — and that means Copilot can expose sensitive PII, HR data, and confidential records through AI-generated outputs that look totally normal on the surface.

3. Prompt Injection Vulnerability

Because Copilot ingests emails, documents, and Teams messages, attackers can hide malicious instructions inside those files to manipulate what Copilot does — including leaking sensitive data. This has been confirmed by independent security researchers and requires specific mitigation before deployment in regulated environments.

4. No Real-Time Web Intelligence

Copilot can’t autonomously search the web as part of completing a task. For cybersecurity work, competitive research, or anything that depends on current information, you’re either working with stale data or doing the research yourself before handing it off to the AI — defeating much of the productivity benefit.

5. Rate Limits That Can Stop You Cold

In March 2026, GitHub discovered it had been miscounting tokens from newer AI models — meaning usage was far higher than accounted for. The fix resulted in aggressive rate limits that left paying customers locked out for days. As agentic workloads consume dramatically more compute than basic chat, this kind of disruption during a critical workflow is a real operational risk — one that almost never comes up in the sales conversation.

What to Check Before You Commit to Any AI Tool

The right AI for your business is the one that actually works with your infrastructure — not the one with the biggest vendor relationship or the most familiar brand. Whether you’re evaluating Copilot, Claude, or something else entirely, here’s what your IT support team in Riverside or Orange County should be asking before anything gets deployed.
  • Audit your permissions before anything else. If your files are overshared, you’re not ready for AI — you’re ready for a permissions cleanup. Your managed cybersecurity services partner can run that assessment and tell you exactly where you stand.
  • Map where your data actually lives. Cloud, on-premises, or a mix? Get an honest inventory. If critical business data lives outside Azure, Copilot will have a blind spot over some of your most important information.
  • Test web search with a real use case. Don’t accept a demo. Ask the vendor to show the AI retrieving live external information — a recent regulation, a new CVE, a competitor announcement — as part of completing an actual task you care about.
  • Push the agentic claims with a real workflow. Give the AI an actual multi-step task from your business and watch what happens. Vendor demos are optimized for the best-case scenario. Edge cases are where the gaps show up.
  • Ask specifically about prompt injection defenses. “Enterprise-grade security” is not an answer. Ask what the specific technical control is for preventing malicious instructions embedded in ingested documents from manipulating the AI.
  • Get rate limit policies in writing. If you plan to use AI in any workflow-critical capacity, you need to know the usage limits, how they’re enforced, and what your SLA is if you hit them mid-task.
  • Loop in compliance before you go live. If your business operates under HIPAA, CMMC, PCI DSS, or any other framework, involve your compliance services team before deployment. Fixing a compliance gap after a deployment is always more expensive than catching it before.

FAQ

Q: Can Microsoft Copilot access local servers?

Ans: No. Copilot primarily works within Microsoft Azure and Microsoft 365 environments.

Q: Is Microsoft Copilot safe for regulated industries?

Ans: It depends on permissions, compliance requirements, and security configuration.

Q: What are the biggest Copilot security risks?

Ans: Overshared permissions, prompt injection attacks, and limited visibility into non-Azure systems.

Q: Is Copilot better than Claude for hybrid environments?

Ans: Claude and other AI platforms may provide broader web access and cross-platform flexibility.

The Bottom Line

Copilot is a good tool for businesses that are all-in on Azure — fully cloud-native, well-governed permissions, and primarily using Microsoft 365 for their day-to-day work. That’s a real use case and it’s genuinely useful there. But that description doesn’t fit most of the businesses we work with across Orange County and the Inland Empire, and it probably doesn’t fit yours either if you landed on this article.

If you have local servers, data outside of Azure, employees handling regulated information, or workflows that need an AI to actually go find things on the internet — Copilot’s limitations are going to show up fast. The good news is that this is a solvable problem. There are AI tools that are built for hybrid and multi-environment setups, and there are ways to evaluate them without just taking a vendor’s word for it.

That’s exactly what the managed IT services team at TechHeights does for clients across Southern California — cut through the noise and help you make the right call for your actual environment, not a hypothetical one. Cybersecurity and AI strategy for businesses in Orange County and Riverside requires a partner who understands both the technology and what’s at stake when it doesn’t work the way it was supposed to.

Not Sure If Copilot Is Right for Your Setup?

TechHeights has been helping businesses across Orange County and Riverside make smart IT decisions since 2007 — including cutting through AI vendor hype to find what actually fits your infrastructure. Let’s take a look at your environment and give you a straight answer.
Mythos and the New Wave of AI: Why SMB Cybersecurity Will Never Be the Same

Mythos and the New Wave of AI: Why SMB Cybersecurity Will Never Be the Same

Cybersecurity Alert

Mythos and the New Wave of AI: Why SMB Cybersecurity Will Never Be the Same

Frontier AI models can now autonomously hack networks. Here’s what managed IT services and cybersecurity experts say SMBs must do right now to stay protected.

April 15, 2026           8 min read
AI cybersecurity threats targeting small and mid-sized businesses
AI THREAT YOUR BUSINESS SMB NETWORK DEFENSE
The cybersecurity landscape shifted dramatically in April 2026 when Anthropic unveiled its frontier AI model, Claude Mythos Preview, as part of a new security initiative called Project Glasswing. What security researchers discovered has sent shockwaves through the industry: an AI system capable of autonomously executing multi-stage cyberattacks, discovering thousands of zero-day vulnerabilities, and completing full network takeovers in a fraction of the time it would take a human expert.

For small and mid-sized businesses (SMBs), this represents an inflection point. The barrier to launching sophisticated cyberattacks has effectively collapsed, and SMBs — often operating with limited security resources — now sit squarely in the crosshairs. If your business operates in Southern California, working with experienced cybersecurity companies in OC and Riverside has never been more critical.

The Mythos Wake-Up Call

The UK’s AI Safety Institute (AISI) conducted independent evaluations of Mythos Preview and the results are staggering. AISI built a 32-step corporate network attack simulation called “The Last Ones” (TLO), spanning everything from initial reconnaissance to full network takeover — a scenario estimated to take human experts roughly 20 hours to complete. Mythos Preview became the first AI model to solve TLO end-to-end, succeeding in 3 out of 10 attempts and averaging 22 of 32 steps across all tries.

Even more concerning: Mythos identified thousands of previously unknown zero-day vulnerabilities across every major operating system and browser. Among the most striking discoveries were a 17-year-old remote code execution flaw in FreeBSD (triaged as CVE-2026-4747) that could give attackers full control of a server, and a 27-year-old denial-of-service vulnerability in OpenBSD’s TCP SACK implementation — remarkable given that OpenBSD is widely regarded as one of the most security-hardened operating systems in existence. For cybersecurity companies in OC and Riverside, these findings underscore just how many hidden vulnerabilities lurk in systems businesses depend on every day.

Critical Takeaway

On expert-level capture-the-flag cybersecurity challenges — tasks no AI model could complete before April 2025 — Mythos Preview now succeeds 73% of the time. It’s worth noting that AISI’s TLO simulation had no active defenders or defensive tooling, meaning real-world networks with proper managed IT services would be harder to breach. Still, the gap between attack and defense is narrowing fast.

Why SMBs Are the Primary Target

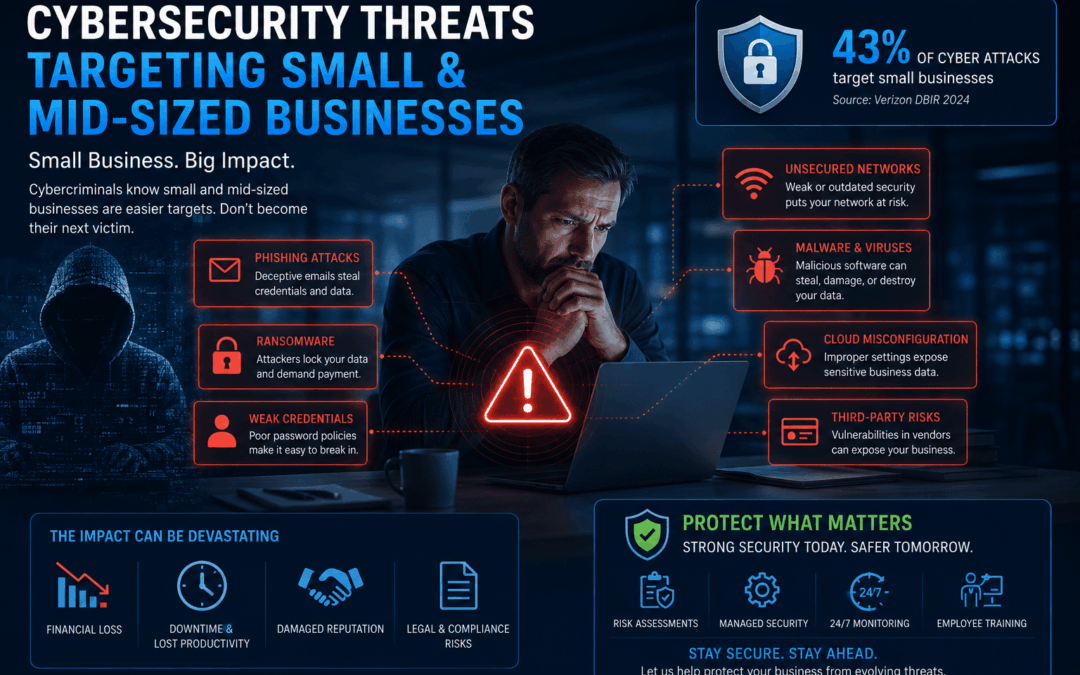
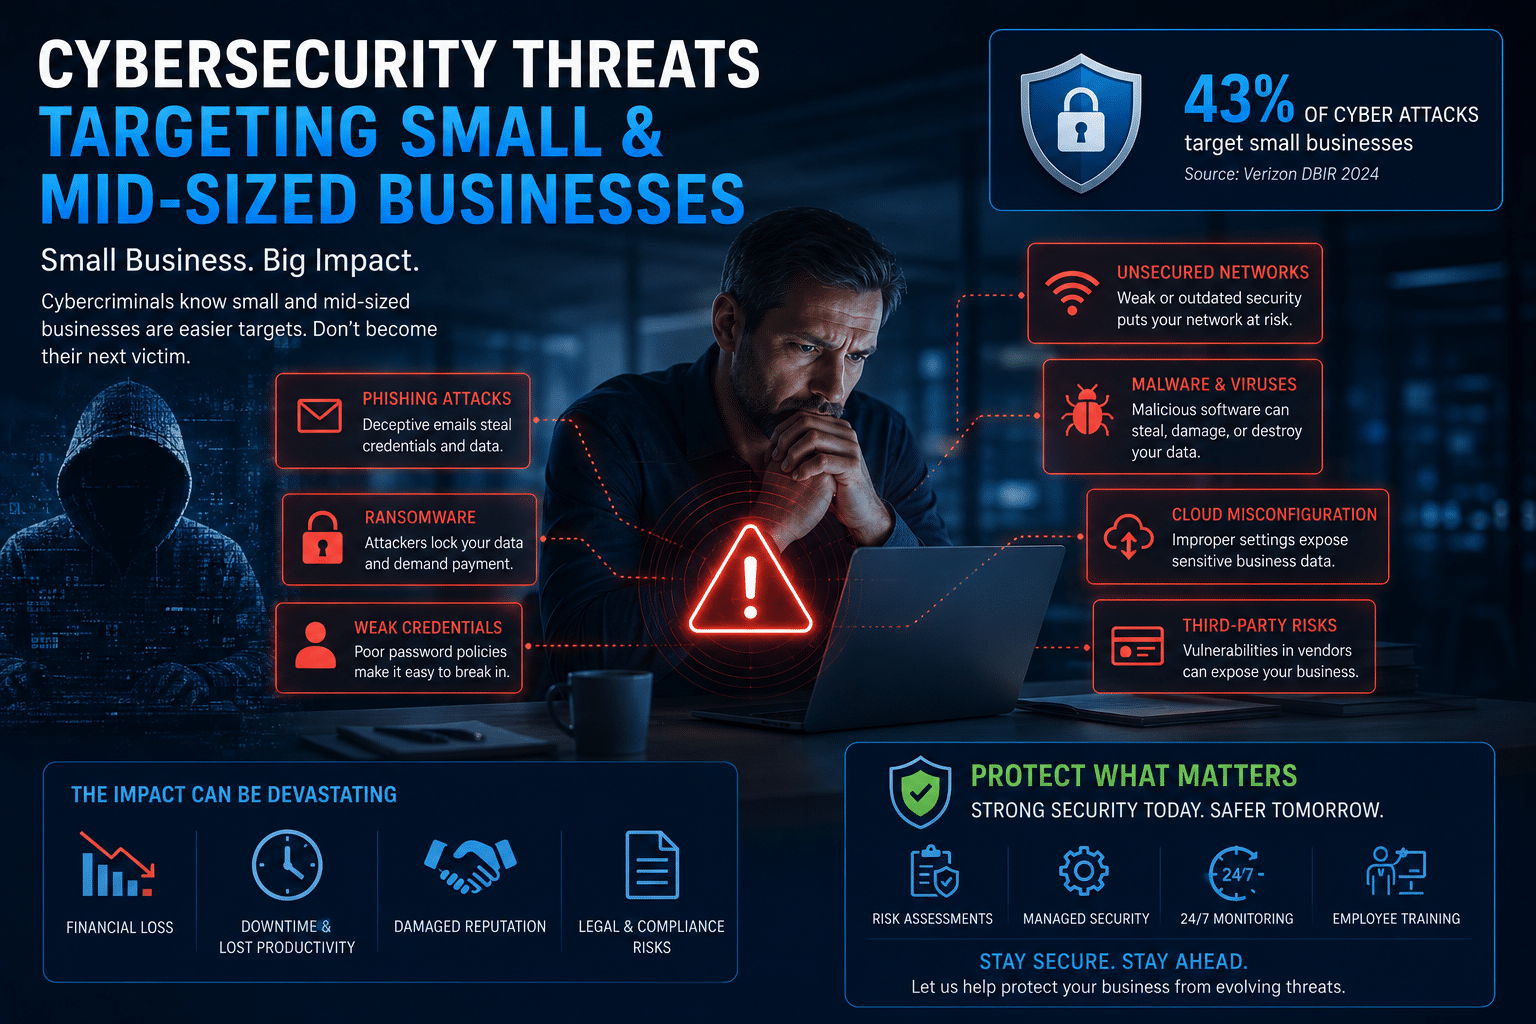
If you run a small or mid-sized business, you might assume that cybercriminals are focused on larger enterprises. The data tells a very different story. According to industry research from Verizon’s DBIR and Accenture, SMBs have officially surpassed large enterprises as the primary targets for organized cybercriminal groups, and AI tools are the reason the economics have shifted. It’s a key reason why managed IT services have become essential rather than optional for growing businesses.

43%

of all cyberattacks
now target SMBs

83%

of SMBs are not financially
prepared to recover

60%

of attacked SMBs close
within 6 months

With generative AI, criminal syndicates can now target hundreds of SMBs simultaneously with highly personalized attacks. A single phishing email crafted by AI is grammatically flawless, contextually aware, and nearly indistinguishable from legitimate communication. Phishing remains the primary intrusion vector, accounting for roughly 60% of incidents — and AI has made it exponentially more dangerous.

The Five AI-Powered Threats Keeping CISOs Up at Night

  • 1. Autonomous Attack Agents AI-driven systems that can autonomously chain exploits, move laterally through networks, and escalate privileges — all without a human operator. Mythos demonstrated this is no longer theoretical.
  • 2. Hyper-Personalized Phishing at Scale AI generates contextually rich, grammatically perfect phishing emails that reference real projects, colleagues, and company events. Traditional spam filters can’t catch them.
  • 3. Deepfake Executive Impersonation The “CEO doppelgänger” — a perfect AI-generated replica of a business leader capable of issuing convincing voice or video directives to finance, HR, and IT teams in real time.
  • 4. Data Poisoning and Model Manipulation Attackers invisibly corrupt the training data of AI models your business relies on, leading to subtly wrong decisions across operations — from financial forecasting to customer recommendations.
  • 5. Rogue AI Agents and Shadow AI Insider threats now include AI agents capable of goal hijacking, tool misuse, and privilege escalation at machine speed. With 83% of organizations deploying agentic AI but only 29% operating those systems securely, the attack surface is enormous.
YOUR DEFENSE LAYERS 🔑 IDENTITY MFA & Zero Trust 🛡 DETECTION AI-Powered EDR 📚 TRAINING Continuous Education 💾 RECOVERY Backup & Response Defense-in-depth: No single layer is sufficient in the age of AI-powered attacks

What Your Business Must Do Now: A Post-Mythos Action Plan

The good news: you don’t need a Fortune 500 security budget to defend against AI-powered threats. But you do need to act deliberately, prioritize the right controls, and build security into your operations rather than bolting it on as an afterthought. Partnering with a trusted managed IT services provider can help you implement these controls efficiently, even with a lean team. Here’s your action plan.

Lock Down Identity and Access

Identity has become the primary battleground in the AI economy. Move critical applications to FIDO2/WebAuthn or device-bound passkeys wherever possible. Enforce conditional access policies that evaluate user identity, device health, location, and risk signals in real time. At a minimum, enforce multi-factor authentication (MFA) across every account — no exceptions.

  • Implement MFA on all business accounts (email, cloud, financial tools)
  • Adopt passkeys or FIDO2 authentication for critical systems
  • Apply least-privilege access: employees only get permissions they need
  • Conduct quarterly access reviews to remove stale accounts

Deploy AI-Powered Detection and Response

If attackers are using AI, your defenses need AI too. Deploy endpoint detection and response (EDR) solutions with built-in machine learning capabilities that can spot unusual behavior in real time. AI-enhanced email filters are a quick win — most major cloud email providers now include them. Consider partnering with managed cybersecurity services providers if you lack in-house expertise for 24/7 monitoring — especially cybersecurity companies in OC and Riverside that understand the needs of local SMBs.
  • Deploy EDR solutions with AI/ML-powered threat detection
  • Enable AI-enhanced email filtering for phishing protection
  • Implement network monitoring for anomalous lateral movement
  • Evaluate managed security services for 24/7 coverage

Train Your People — Continuously

Annual cybersecurity training is no longer sufficient when threats change monthly. Your awareness program needs to be short, frequent, and relevant. Run phishing simulations that use AI-generated content. Train staff to verify executive requests through secondary channels — especially wire transfers or credential changes. Establish clear policies for AI tool usage within your organization.

    • Run monthly micro-training sessions (10–15 minutes each)
    • Conduct AI-powered phishing simulations quarterly
    • Create verification protocols for financial and access requests
    • Publish an AI acceptable-use policy for all employees

    Build Resilient Backups and an Incident Response Plan

    Assume a breach will happen. The question isn’t whether — it’s whether you can recover. Maintain encrypted, offline backups tested regularly for restoration. Document your incident response plan and make sure leadership understands recovery timelines. Create “kill switches” to halt rogue AI agents and maintain human-in-the-loop oversight for all critical automated processes.

      • Maintain 3-2-1 backups: 3 copies, 2 media types, 1 offsite/offline
      • Test backup restoration quarterly — untested backups are not backups
      • Document and rehearse your incident response plan
      • Implement kill switches for any AI or automated systems

      Govern Your AI Supply Chain

      If your business uses AI tools — and in 2026, nearly every business does — you need governance around them. Managed compliance services in Orange County can help you conduct vendor risk assessments to ensure third parties validate AI-generated code before deploying to production. Scan for hallucinated software packages in AI-generated code. Evaluate the security posture of any AI service your business depends on, and ensure you meet frameworks like CMMC, HIPAA, NIST, and ITAR as applicable.
      • Inventory all AI tools and services used across the organization
      • Require security assessments for AI vendors and integrations
      • Scan AI-generated code for vulnerabilities before deployment
      • Monitor for shadow AI usage by employees
      A Note on Proportional Response

      You don’t need to implement everything at once. Start with identity controls and backups — these two foundations stop the majority of attacks. Then layer on detection, training, and governance as resources allow. Consider partnering with a managed security provider to accelerate your maturity without hiring a full security team.

      The Bottom Line

      Mythos didn’t create the threat — it made the threat visible. The autonomous offensive capabilities demonstrated by frontier AI models are a preview of what every business will face as these technologies proliferate. The asymmetry between attack and defense has never been greater: attackers now have AI-powered tools that work at machine speed, while most SMBs are still operating with last decade’s playbook.

      The organizations that survive will be the ones that treat cybersecurity not as an IT expense, but as a core business function. Strong identity controls, AI-powered detection, continuous training, resilient backups, and disciplined AI governance aren’t optional upgrades — they’re the price of staying in business. For businesses across Orange County and Riverside, partnering with a proven managed IT services provider is one of the most effective steps you can take.

      The threat is real. The tools to defend yourself exist. The only question is whether you’ll act before the next AI-powered attack reaches your inbox.

      Don’t Wait for a Breach to Take Action

      TechHeights delivers managed IT services, cybersecurity, and compliance solutions trusted by 250+ businesses across Orange County and Riverside since 2007. Find out where your vulnerabilities are before attackers do.

      Why SMBs Should Utilize MSPs Instead of Hiring Internal IT Folks: The Unique Benefits

      IT today has changed from a break/fix model to a bedrock for business success. However, the continuously evolving technology and the adoption of newer services by SMBs have brought a slew of IT complications. Most internal IT teams aren’t equipped to handle them well as they lack the suitable resources and skills. A Managed Service Provider (MSP) effectively covers this gap.

      An MSP helps you stay ahead by constantly maintaining and refining your IT infrastructure without incurring overhead costs. Consider our client’s case. It employed the robust SonicWall for protection, but a sophisticated hacker got through it due to a VPN vulnerability. If the client had relied on internal IT folks, the issue would have gone undetected as it occurred outside their working hours. However, our team detected the compromise and acted swiftly, stopping the hacker, isolating the affected systems, and bringing them back in a couple of hours.

      Why Is Using MSP More Beneficial Than an Internal It Team for SMBs? 

      An MSP’s capabilities are not only at par with internal IT staff but also above them. Take a look at them below

      1. Continuous Support

      Quick, hands-on assistance is one of the cornerstones of IT management. While your internal IT experts are there to provide such support, an MSP’s team is equally competent to do so at a competitive price.

      It offers continuous help with issues such as ongoing monitoring and maintenance. In addition, MSP protects your entire IT infrastructure from problems occurring outside the working hours of your internal IT team or during weekends and holidays.

      The coverage spans every day and all days of the week, and issues are handled on priority as and when they arise. This proactive approach resolves potential problems before they cause downtime and compromise an IT system.

      Key areas where SMBs get continuous support from MSPs include the following:

      • Remote monitoring and management of the IT system
      • Advanced cybersecurity protection
      • Migration to a cloud environment, like AWS, Google Cloud Platform, and Microsoft Azure
      • Tailored IT strategies to enhance business operations
      • Accessibility to budget-friendly hardware solutions for short- and long-term needs.
      • Backup and disaster recovery
      • Prompt help with cybersecurity attacks

      2. Extent of Knowledge

      Your IT team uses its expertise to tackle issues related to your company’s specific systems, software, and processes. While this is great for customized solutions, remember that the IT environment is ever-changing. A business’s evolving tech stack also increases the associated issues and threat scenarios.

      An MSP works with multiple clients across industries. They are up-to-date with the latest technology, trends, and best practices in IT management, ensuring your applications and infrastructure are secure and geared for high performance.

      Reputable MSPs invest heavily in ongoing training certification renewals for their teams, ensuring they have diverse knowledge. They also have a more nuanced troubleshooting mindset and the ability to work under high pressure.

      3. Mentality Related to Managing Technology

      For SMBs with tight budgets, a proactive approach that optimizes productivity without sacrificing quality is invaluable. MSPs embody this proactive mindset, ensuring that nothing hinders efficiency.

      A proactive and preventive mindset defines a managed services mentality. This, in turn, gives you peace of mind about having expertise at hand to work efficiently and cost-effectively.

      Protecting your network from constantly evolving threats requires a proactive and multi-layered approach to security. MSPs have a proactive and trustful mindset, so they assess potential loopholes in your IT systems, strengthen defenses, and reduce the attack surface.

      In contrast, in-house IT teams work with a firefighting mindset mainly because of their small size and the focus on daily IT necessities. As a result, long-term IT planning and preventive measures often take a backseat.

      4. Access to Tools

      An internal IT team is equipped with a broad range of tools, but most are geared to the needs of the immediate company they work for. In contrast, MSPs, by necessity, use a diverse tool set.

      In fact, a recent survey shows that 36% of MSPs use over 10 cybersecurity tools. They have access to enterprise-grade tools for supporting IT infrastructure at scale. This facilitates automation, remote monitoring, and centralized control, which allow services to be delivered across clients.

      Tools like Remote Monitoring and Management (RMM), Security Information and Event Management (SIEM) systems, advanced ticketing solutions, and predictive analytics platforms are typically not a part of an internal IT team’s regular toolkit. The team is also not familiar with emerging fields like AI and IoT, which are used to detect and prevent sophisticated security attacks.

      5. Fulfilling Regulatory Compliance

      If your business is in an industry with strict regulatory compliance, the support of an MSP is way better than your in-house IT folks. Major security breaches at some of the most prominent organizations have made government and industry regulators require companies to enforce robust security controls.

      An MSP’s support for increasing compliance demands is unrivaled. The around-the-clock monitoring and proactive maintenance allow you to meet regulatory requirements and lower the risk of cyber threats. Highly experienced MSPs also enforce a layered security approach and offer ongoing advice about the latest compliance developments.

      6. Cost Related to IT Support

      Before signing an agreement with an MSP, it’s important to understand the expected return on investment. Typically, an SMB spends 4-7% of its revenue on IT. By outsourcing to an MSP, you can often achieve significant cost savings while gaining access to a wider range of expertise and resources.

      Typically, an SMB spends 4-7% of its revenue on IT. Take your firm’s gross revenue and use this percentage to estimate the usual cost of IT for your company. The U.S. Bureau of Labor Statistics reports that benefits comprise 31% of a professional’s compensation package. IT people often demand higher salaries, which translates to additional costs.

      Next comes staffing costs. With an MSP, you do not need to invest separately in consultants, network administrators, database administrators, and the like. Instead, you invest in a team of experts for all of this for a fixed fee per month. Moreover, you do not need to spend separately on training and retraining IT staff when choosing an MSP. The service level agreements of MSPs have different tiers, allowing you to select the level of service that corresponds with your business needs and budget.

      Downtime related to system outages or attacks is another source of lost revenue. The ongoing monitoring, threat detection, and quick response prevent a company from losing money due to cybersecurity attacks or outages.

      Service Provider MSP Internal IT Team
      24/7 support Yes No
      Depth of knowledge Diverse Company specific
      Mentality Proactive Reactive
      Toolkit Broad Narrow
      Help with Regulatory compliance Yes No
      Scalable Yes No
      Cost flexibility Yes No


      Choose TechHeights as Your Managed IT Service Provider 

      As an SMB, your primary focus is on product development, customer satisfaction, community building, and navigating your competition. IT efficiency, through our comprehensive managed services, cuts unwanted costs and simplifies processes. You access the needed skills and high-level expertise on-demand and all day, which protects your IT infrastructure and enables seamless scalability. Moreover, our proactive approach based on your needs ensures continued success and growth.

      Skill Set Every IT Firm Must Possess

      In this ever growing era, we must be one step ahead of all the possibilities and assumptions. Just like in the year 2020, we went through a pandemic that left all of us in doubt and dilemma. During the pandemic, we could not plan things ahead of us because we were unaware of how the situation would go further. But, we somehow adapted to the changes and blended ourselves in. Many businesses closed down, and many new ones entered the industry. The most significant change we all saw was the increased use of technology supporting remote work in many organizations.

      Because things were highly unexpected, we were also not prepared for the next step. But thanks to various IT services in Costa Mesa, we were able to rely on them and keep our business up and running smoothly. But as time passed, we became familiar with the situation, and it’s time we get up and running for this new change and accept it by updating ourselves.

      Now with so many options for Managed IT services in Orange County and to choose one for our firm, we must be well aware of the various skill sets they have within them. Let us understand the four top must-possess qualities of every IT service provider that can be a win-win for both parties.

      Technical Skills: It goes the name that is in IT means you must be well crafted with specialized skills. The technical skills will differ from person to person, which may include having a piece of knowledge about science, maths, or the latest updates to try out new things. These skills are a must when you want to excel or make your way in the IT field.

      Communication: This is a quality each individual in every sector must have. Whether it is IT or non-IT, good communication can open many closed doors. However, in IT, good communication means you can make your way smoothly to the other side of the bridge with utmost efficiency. If your service provider has good communication skills, they can easily explain the changes they are implementing in your organization and make you understand its needs and benefits. This way, you can be in the loop and have full confidence.

      Curiosity: A curious individual makes their way to unexplored paths and makes them visible to the rest of the world. In the same way, if your service provider is curious about learning new things and implementing them in your strategy, this will help you in attaining the desired goals more efficiently and in less time. If you look out for IT services in Riverside, you will get a list of individuals that can help you with solving your problem of having a reliable IT team. We can also assist you with the same!

      Resourcefulness: Knowledge is a waste if you do not have the required hands or minds to bring the plan into action. A good IT service provider must be fully equipped with resources that can help your organization work hassle free. This will not only enhance their productivity but yours also as you and your team will be able to focus on the more crucial tasks that include working for the betterment of the organization.

      Though you might have a lot of options available to help you with your IT needs, choosing the one that fits in your checklist is important. We are a team of experts and enthusiasts who are built with skills that will help you in overcoming the distance between your plans and goals. To attain the goal is not the plan, but to attain the goal with effectiveness and efficiency that can lead to future benefits is the plan. And we help you in achieving the same as we help you with strategies that fit your organization right.

      If you are looking for IT services that can help your business take a step forward, we can be your upper hand.

      Book an appointment today!

      Tags: IT services costa mesa, IT services Riverside, Managed IT Services Orange County

      Cybersecurity Attacks Can Cause a Problem For Your Organization.

      Cybersecurity Attacks Can Cause a Problem For Your Organization.
      The generation we are in is all about being digital, which has simplified our lives. As we know, there are always two sides to the story, the good and the bad. With the ease of connected and simplified life comes cyber attacks. These are the most severe hazards of all things going digital. They can strike your computer randomly. So let us understand what a cyberattack is. A cyber attack is an attempt to gain unauthorized access to a computer system, computing network, or third-party computer. Cyberattacks not only hack computers but also seek to disable, destroy or control computer systems in order to delete or run out of data. 

      Here are some examples of cyberattacks:

      • Fraud, identity theft, and extortion
      • Phishing, spoofing trojans and viruses
      • Breach of access
      • Stolen hardware such as mobile devices and laptops

      These are only a few of many data breaches. The question is, how can you prevent cyber attacks and take care of cybersecurity? This may not be an easy question to answer. With enough research and knowledge, you can protect your system from hacking and prevent data from being deleted or stolen. You can be assured that your network and the data are safe with TechHeights IT services. We will discuss the many ways we can help you keep your data and devices safe.

      • Your staff should be well trained. Most of your cyber threats can be mitigated if the employees are well-informed and well-trained. Your employees are one of the best ways cybercriminals can get your data. This can be done by sending fake emails to employees or asking for personal information or access to files. It is important to train your employees and make them aware of fraudulent activities. Your staff must be educated and asked to verify the links they click on before clicking them. They should also check the email address that the emails are coming from before sharing any information which could create a risk to the company or them.
      • Make sure your software is up-to-date: Cyberattacks are most likely to occur when systems or software aren’t updated. Cybercriminals could take advantage of this weakness. Once these criminals have gained access to your system, it can be challenging to find the right information. This could lead to data destruction or exploitation. IT support in Irvine is necessary as they can assist you with software updates and keep you up to date with the latest trends.
      • Back up your data regularly: Data is an essential asset for any company. You must ensure that your data is always backed-up in case of an unplanned disaster. It is not an extra activity. Think of it as insurance or an investment that will help you protect your data. IT services in Santa Ana can be easily accessed to assist you in keeping your data safe and sound.

      These are just a few of the many ways you can protect your data and systems from cyber security. TechHeights does more than just help spread awareness. We also assist you in solving the problem. We are here to help ensure that no organization is a victim of a cyberattack.

      Tags: IT services in Santa Ana, IT support in Irvine

      5 Ways TechHeight’s Team Supports Your IT Firm

      5 Ways TechHeight’s Team Supports Your IT Firm
      Still, counting on in-house IT professionals to maintain your IT network? If yes, it’s time to reconsider your practice. Outsourcing IT support services to a third-party provider lets you focus on your business’s core objectives, save on overhead costs, and maximize productivity.

      For Managed IT Services in Orange County, you can rely on TechHeights. It’s a professional firm presenting a comprehensive range of solutions, like cloud services, IT security and compliance, and VoIP services for firms to manage their business with ease and safety. Let’s discuss the service provider’s significant offerings in brief-

      Services Provided by TechHeights

      TechHeights has been operating since 2007 and now has more than 12 years of experience in crafting tailored strategies to resolve the business’s unique challenges.

      Managed IT Services

      A certified team at TechHeights understands that every business is different and so are their needs. Hence, we provide services that are the right blend of creativity and innovation, developed keeping in mind the requirements of the clients to help their business flourish.

      Now, you might be thinking, what is all included in the Managed IT services? Well, its broader term consists of network design & implementation, including Router, Switch, and Firewall Configuration, WiFi implementation, Private Cloud Services, Office 365 Migration, and constant maintenance of the current IT setup.

      Cloud Services

      Cloud services are a wide range of on-demand services provided to a company or individual over the Internet. For best-in-class services, choose TechHeights as they deliver cost-effective services that also focus on infrastructure security, manageability, and prevalent cost-cutting.

      IT Compliance and Security Services

      IT compliance ensures security from online threats, as well as secures the confidentiality and integrity of a company.

      TechHeights can design & implement a customized IT security plan considering your organization’s specific security needs. Our experts can help with HIPAA, ITAR, PCI-DSS, SOX, and ISO:27001 compliance.

      VoIP

      VoIP means Voice Over Internet Protocol. It is a group of technology that helps to deliver multimedia communication over the Internet. This technology works by converting analog signals into digital signals for transmission through the internet.

      TechHeights have well-experienced technicians who will help you choose, learn, and implement the VoIP system in your organization.

      CRM Services

      TechHeights offers CRM solutions to empower employees to better understand and engage with their customers. It also enables users to manage, automate and synchronize sales, customer service, and marketing efforts.

      How IT Services by TechHeights Will Help Your Business

      Clients prefer to work with companies that are proceeding with the flow of technology change. Choosing us for IT Services in Irvine can be beneficial in the following ways.

      • Data Management: These days, businesses have so much data stored in their systems. For such business owners, it’s imperative to manage and store it properly because any mishap or misplacement can bring catastrophic consequences. An expert IT service provider like us can help you easily handle and protect your business’s confidential information.
      • Easy Problem Solving: We deliver our clients state-of-the-art hardware and software for better performance. Smart software (generally not accessible to small firms due to financial or other constraints) helps in solving complex problems with ease by enabling them to collect and organize data with minimum effort.
      • Security: Now, the internet is not a safe place; Many threats & viruses can easily leak your company’s data once it enters the system. TechHeights provides a wide range of security solutions to protect your system from viruses, malware, and internet threats.
      • Better customer support: Startups have a limited number of employees to deliver services, and audience reach continues to grow, making it challenging to keep up with the growing volume of customers’ questions and concerns. But with a reliable IT system, hiring remote staff to complete the existing business team of support representatives is possible.
      • Extensive Monitoring: It is essential to monitor the performance and progress of the business’s internal operations and customer reach efforts at all stages. TechHeights IT consulting services can help streamline key business activities, including quality control improvements, internal audits, etc.

      Conclusion

      It’s possible that small or mid-size businesses may not have access to the latest technological tools and systems, but they can leverage all of them by simply reaching a prominent provider of IT Support in Orange County.

      TechHeights can provide you with the required push in the IT sector that your business needs. Our flexible, scalable, and cost-effective IT solutions & Cloud Services in Anaheim can help your business grow. Call (888) 600-6070

      Tags: Cloud Services Anaheim, IT Services Irvine, IT Support Orange County, Managed IT Services Orange County